Malacañang confirmed on Thursday that the government is fully prepared to handle any cyberattack, describing such incidents as nothing new after at least 10 official government websites were recently targeted.
MANILA, Philippines — Malacañang assured the public on Thursday that the national government is fully equipped and ready to address any cyberattack threats, following recent security breaches that affected at least 10 government websites.
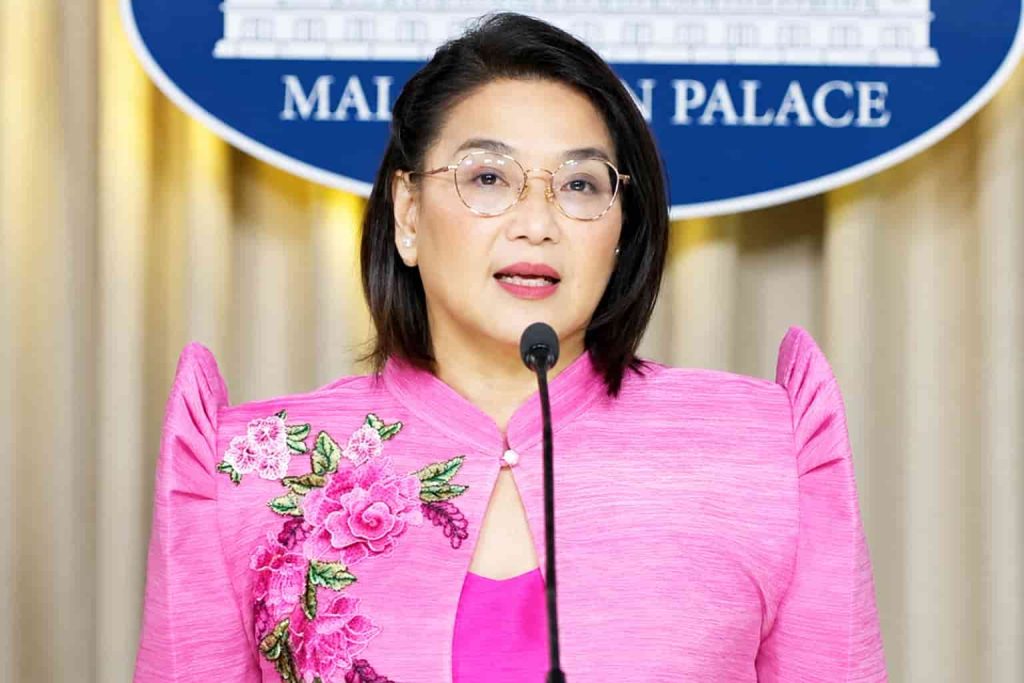
Presidential Communications Office Undersecretary and Palace press officer Claire Castro gave the assurance during a regular press briefing, emphasizing that such incidents are not new to government agencies.
“Oo, alam ng Pangulo ang mga nangyayaring kaganapan, lalong-lalo na sa mga nangyayari sa mga ahensiya,” Castro stated, confirming that President Ferdinand R. Marcos Jr. is fully aware of the situation across government agencies.
“May pagkakataon na noon pa man may mga ahensiyang naha-hack, pero agad itong natutugunan. Handa po ang gobyernong tumugon sa mga cyber attack na ito na ginagawa, pagha-hack ng mga website, handa po ang gobyerno,” she added.
READ MORE ARTICLES:
- Palace: Gov’t fully prepared to counter cyberattacks
- Tinio Questions Pax Silica Deal Amid Uncertain US Congressional Support
- PAGCOR Faces Audit Over ₱412 Million in Undelivered Donation Goods
- Judiciary Marshals Join Probe Into Fatal Ambush of Basilan Judge Joseph Wee Sit
- Sara Duterte Defense Mounts Fight as Impeachment Trial Intensifies
- DFA Urges Government Officials to Align Public Statements With Marcos’ Foreign Policy
Castro explained that similar hacking attempts have occurred in previous years and were promptly resolved by the government’s technical teams. Her remarks came in response to renewed concerns after multiple official government portals went offline or were defaced in the latest wave of cyber incidents.
While the Palace did not disclose further details on the extent of the damage or the identities of the groups behind the attacks, it emphasized that response mechanisms are already in place and activated whenever necessary. Authorities also reminded the public to remain vigilant and rely only on verified official channels for important government updates.
Philippines Faces Growing Government Cybersecurity Threats
A series of cyberattacks and reported data security incidents involving Philippine government agencies has renewed concerns over the country’s ability to protect digital systems and sensitive information. The incidents have included website defacement, alleged unauthorized access and the reported acquisition of government database backups.
The latest developments emerged in November 2026 after the National Privacy Commission (NPC) confirmed that it had received personal data breach notifications from 10 government agencies. These included the Presidential Commission on Good Government (PCGG), Department of Information and Communications Technology (DICT), Department of Labor and Employment (DOLE) through its Bureau of Local Employment, Bureau of Internal Revenue (BIR), Philippine Amusement and Gaming Corp. (PAGCOR), Department of Justice (DOJ) through its Office for Alternative Dispute Resolution, Securities and Exchange Commission (SEC), Philippine Coast Guard (PCG), Department of Trade and Industry (DTI), and the DOST-Philippine Institute of Volcanology and Seismology (PHIVOLCS).
The NPC said the reported incidents were being assessed to determine how the breaches occurred, what information may have been affected, the possible consequences for individuals and how the concerned agencies responded. The notifications followed reports of alleged cyberattacks against several government institutions on November 5, although authorities emphasized that claims made by hackers must be distinguished from breaches that have been independently confirmed.
The Cybercrime Investigation and Coordinating Center said it was examining allegations involving about 20 government agencies. CICC Executive Director Renato Paraiso also said investigators were determining whether some of the information being presented as newly stolen data could actually be older datasets that had been reused or recirculated online.
Among the allegations reported in November were possible compromises involving government systems connected to the Office of the Vice President and the Philippine Air Force. However, some of these reports had not been independently verified. The appearance of government-related files online, by itself, does not establish that an official government system was successfully breached.
The NPC initially said on November 6 that it had not yet received personal data breach notifications from the agencies involved in some of the allegations. The commission said it would work with the concerned institutions to verify the reports and determine whether personal information had actually been compromised. By November 10, however, the privacy regulator confirmed that 10 government agencies had formally submitted breach notifications. The NPC said reporting such incidents is part of government agencies’ responsibilities under the Data Privacy Act of 2012.
Another cybersecurity concern emerged in October involving databases connected to the country’s overseas employment system. Cybersecurity researchers reported that an unidentified operator had obtained 27 Microsoft SQL Server backup files with a combined size of about 68.837 gigabytes. The filenames reportedly pointed to systems associated with the former Philippine Overseas Employment Administration, whose functions have since been integrated into the Department of Migrant Workers.
The National Privacy Commission opened an investigation into the reported database incident. However, researchers did not examine the contents of the backup files, and authorities had not determined how the files were initially accessed or where they were transferred. As a result, the reported 69GB should not be considered a confirmed volume of exposed personal information. The incident nevertheless raised concerns because overseas-employment systems may contain information relating to Filipino migrant workers, including employment and assistance records.
Government websites also faced cyber incidents earlier in 2026. In June, the official websites of the Senate and House of Representatives were subjected to defacement attacks. The DICT said its initial assessment found no evidence that confidential or sensitive information had been compromised in the Senate incident.
The House of Representatives website was also defaced, prompting the DICT to activate its incident-response procedures. Authorities said the affected pages mainly contained publicly available information and that initial findings did not indicate that sensitive government data had been compromised. The National Bureau of Investigation later said it had identified individuals suspected of involvement in the attacks, although their identities were not immediately disclosed because the investigation was still ongoing.
The incidents showed that cyberattacks do not necessarily involve the theft of confidential information. Website defacement, which involves changing the appearance or content of an official website, can disrupt government services and affect public confidence in digital government platforms.
The Philippines had already experienced a major government cybersecurity incident in September 2023, when the Philippine Health Insurance Corp. was hit by a Medusa ransomware attack. PhilHealth confirmed that the attack affected information stored on some servers and local workstations. The agency reported the incident to the DICT, NPC and law-enforcement authorities and took steps to isolate the affected systems.
PhilHealth officials later estimated that the personal information of around 13 million individuals had been compromised, with the potential number of affected people reaching between 13 million and 20 million. The incident demonstrated the serious risks faced by government institutions that maintain large amounts of personal information.
The Philippine Statistics Authority also investigated a reported data breach in October 2023 involving its Community-Based Monitoring System. The PSA said its initial assessment identified the CBMS as the affected system and that it coordinated with the NPC, DICT, Philippine National Police and National Bureau of Investigation during the investigation.
The PSA also clarified that its Philippine Identification System and Civil Registration System were not affected. The agency said the information involved in the CBMS incident remained within its system and that backup copies were available.
The country’s history of government cyber incidents extends further back to March 2016, when the Commission on Elections experienced a cybersecurity incident involving the defacement of its public information website and the alleged theft of election-related data. Hackers claimed to have obtained the entire COMELEC database, although the commission later clarified that the leaked information did not constitute its complete database.
COMELEC said the compromised information included records from systems such as the Precinct Finder, including names, dates of birth, gender, civil status, addresses and other voter-related information. The incident became widely known as “Comeleak” and remains one of the most significant government data-security incidents in the country’s history.
The series of incidents recorded between 2016 and 2026 demonstrates how cyber threats against Philippine government institutions have continued to evolve. Earlier attacks were often associated with website defacement and large-scale data exposure, while more recent incidents have involved ransomware, alleged unauthorized access, database theft and other sophisticated cyber threats.
Authorities have also urged the public to remain cautious about hacking claims circulating online. The CICC has warned that some datasets presented by alleged hackers may consist of old information rather than evidence of newly compromised government systems.
For ordinary Filipinos, the possible consequences of government data breaches can extend beyond affected websites and databases. Personal information that is exposed or stolen could potentially be used for phishing, identity theft, fraud and other cybercrimes.
The recent incidents underscore the importance of strengthening cybersecurity measures across government agencies, securing database backups, conducting regular security assessments and improving the speed of responses to suspicious activity.
The National Privacy Commission continues to assess the reported November incidents, while cybercrime authorities work to determine the source of the attacks and establish whether the information circulating online is authentic, newly obtained or recycled from previous data exposures.
- Italy Fines Meta €805 Million Over Privacy Violations
- LEPT Results September 2026 Teachers Board Exam in Elementary & Secondary
- Miss Universe 2026 Faces Controversies Ahead of Coronation
- Telegram Founder Pavel Durov Funds Free IVF for Women Using Donated Sperm
- LEYTE: Tacloban-Born Chef Earns Prestigious Michelin Star